
I used to think wallet security came down to one rule: never share your seed phrase, and you’re safe. I don’t believe that anymore.
The more incidents I’ve read through, the clearer it becomes that the biggest thefts in crypto history didn’t come from stolen passwords or leaked recovery phrases at all. They came from something far more mundane, a signature request, a token approval, a permission click that looked routine enough that nobody thought twice about it. That’s the part that unsettles me most. These attacks don’t break into your wallet. You let them in, one signature at a time, without ever realizing what you actually agreed to.
Why These Attacks Don’t Need Your Seed Phrase
Every crypto wallet security warning tells you the same thing: guard your seed phrase like your life depends on it. That advice isn’t wrong, but I think it’s created a dangerous blind spot. Once someone internalizes “never share my recovery phrase” as the whole security model, they stop scrutinizing everything else a wallet asks them to approve. And that’s exactly the gap attackers have learned to exploit. A malicious actor doesn’t need your keys if they can simply get you to authorize them to move your funds directly, using the wallet’s own legitimate permission system against you. Here are five of the most common ways that happens, each one backed by a real incident.
1. Malicious Token Approvals: The BadgerDAO Playbook
The clearest example of this entire category, and still one of the largest, is the BadgerDAO hack from December 2021. Attackers compromised BadgerDAO’s Cloudflare account and injected a malicious script directly into the project’s legitimate front-end website, one that users had been safely interacting with for months.
When users went to make ordinary deposits or withdrawals, the injected script quietly inserted an additional request asking them to approve an unlimited spending allowance for the attacker’s address on their ERC-20 tokens. According to ZenGo’s analysis of BadgerDAO’s technical post-mortem, the script ran periodically over roughly three weeks before the attacker triggered the drain, ultimately pulling in around $120 million from nearly 500 wallets.
What makes this case so important to understand is what it proves: the smart contracts were never touched. The audits were clean. Nothing about the website itself looked wrong, correct URL, valid certificate, familiar interface. The only thing that changed was a permission prompt asking for more access than the transaction actually needed, and hundreds of experienced DeFi users approved it anyway because it looked like routine wallet activity. It’s also why security-conscious users now regularly check what a wallet has approved in the past. Ethereum’s own block explorer, Etherscan, offers a free Token Approval Checker tool that lets anyone review and revoke standing approvals tied to their address, something worth doing periodically even outside of an active scare.
2. Blind Signature Requests: When “Sign This Message” Isn’t Harmless
Token approvals aren’t the only mechanism attackers lean on. A quieter, arguably more dangerous method involves signature requests, particularly the kind generated through eth_sign or off-chain signing standards like EIP-712 permits. Unlike an on-chain transaction, a signature request often doesn’t cost gas and can look, on the surface, like a harmless proof of identity or a simple login confirmation. That’s precisely what makes it so exploitable. A malicious dApp can construct a signature request that, once signed, functions as a valid authorization to transfer specific tokens out of your wallet, without you ever seeing a transaction that clearly says “send my funds.”
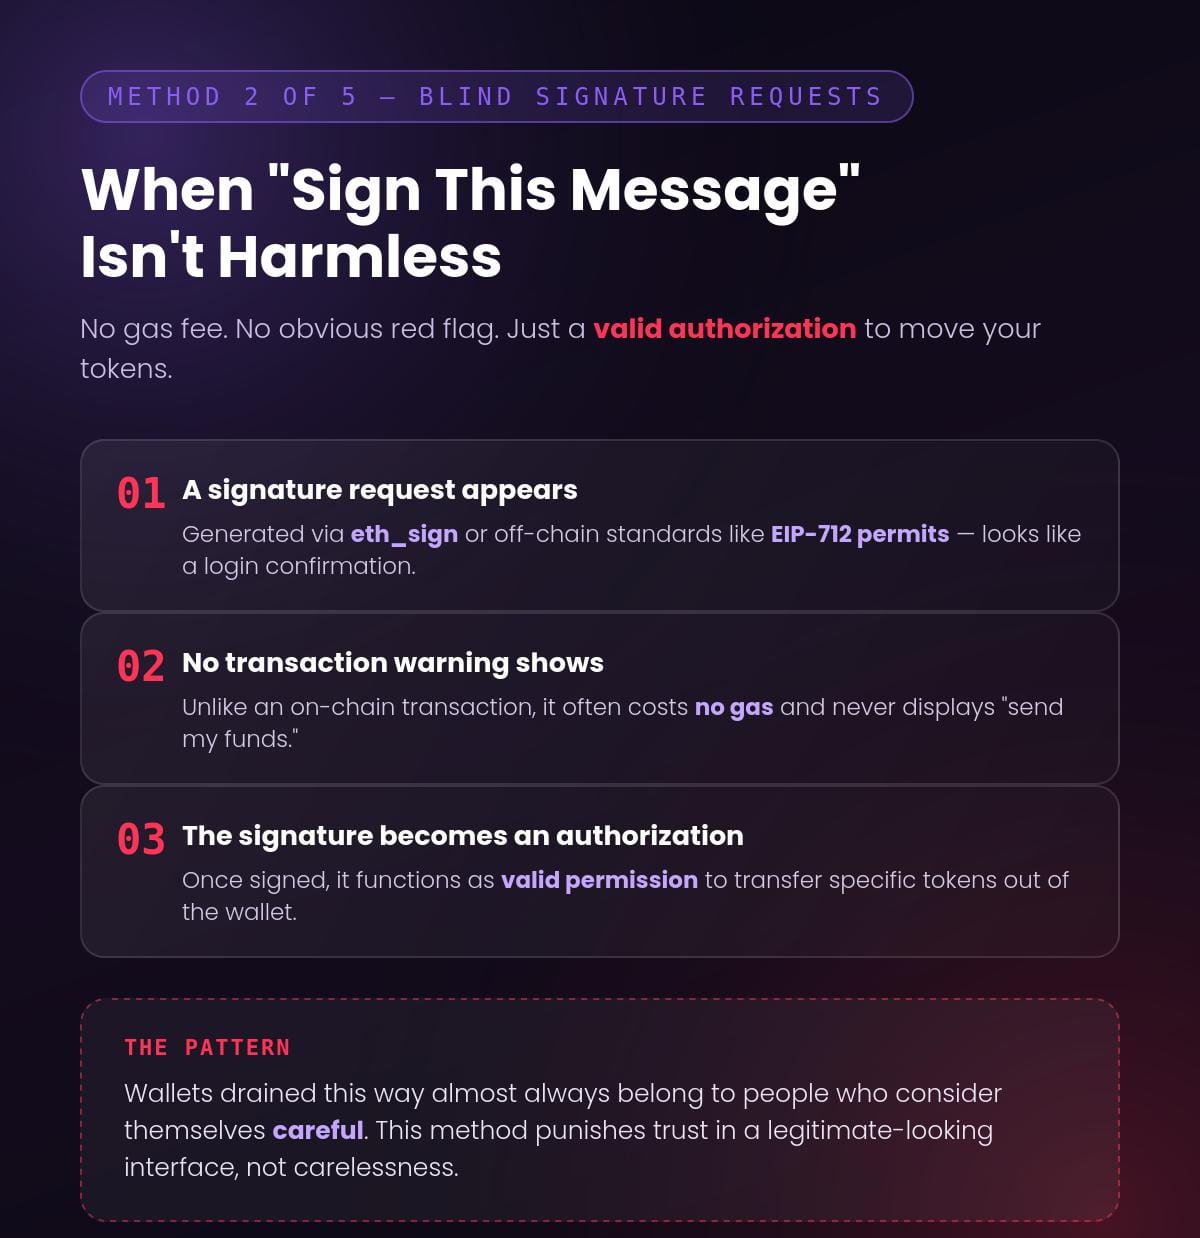
Security researchers refer to this broader category as “ice phishing,” a term that gained traction specifically because of how the BadgerDAO incident itself functioned, tricking users into signing permission grants rather than stealing credentials outright. I’ve read through enough of these reports to notice a pattern: the wallets that get drained this way almost always belong to people who consider themselves careful. Blind signing doesn’t punish carelessness so much as it punishes trust in an interface that looks legitimate.
3. Malicious dApp Permissions Through Fake WalletConnect Sessions
The third method operates at the connection layer rather than the transaction layer. Fake or cloned decentralized applications, often distributed through phishing ads, fake Discord announcements, or spoofed WalletConnect prompts, are built to look identical to popular, trusted platforms. Once a user connects their wallet, the fake dApp requests a batch of permissions dressed up as standard onboarding steps, permissions that, when combined, give the attacker’s smart contract broad authority over the user’s token balances.
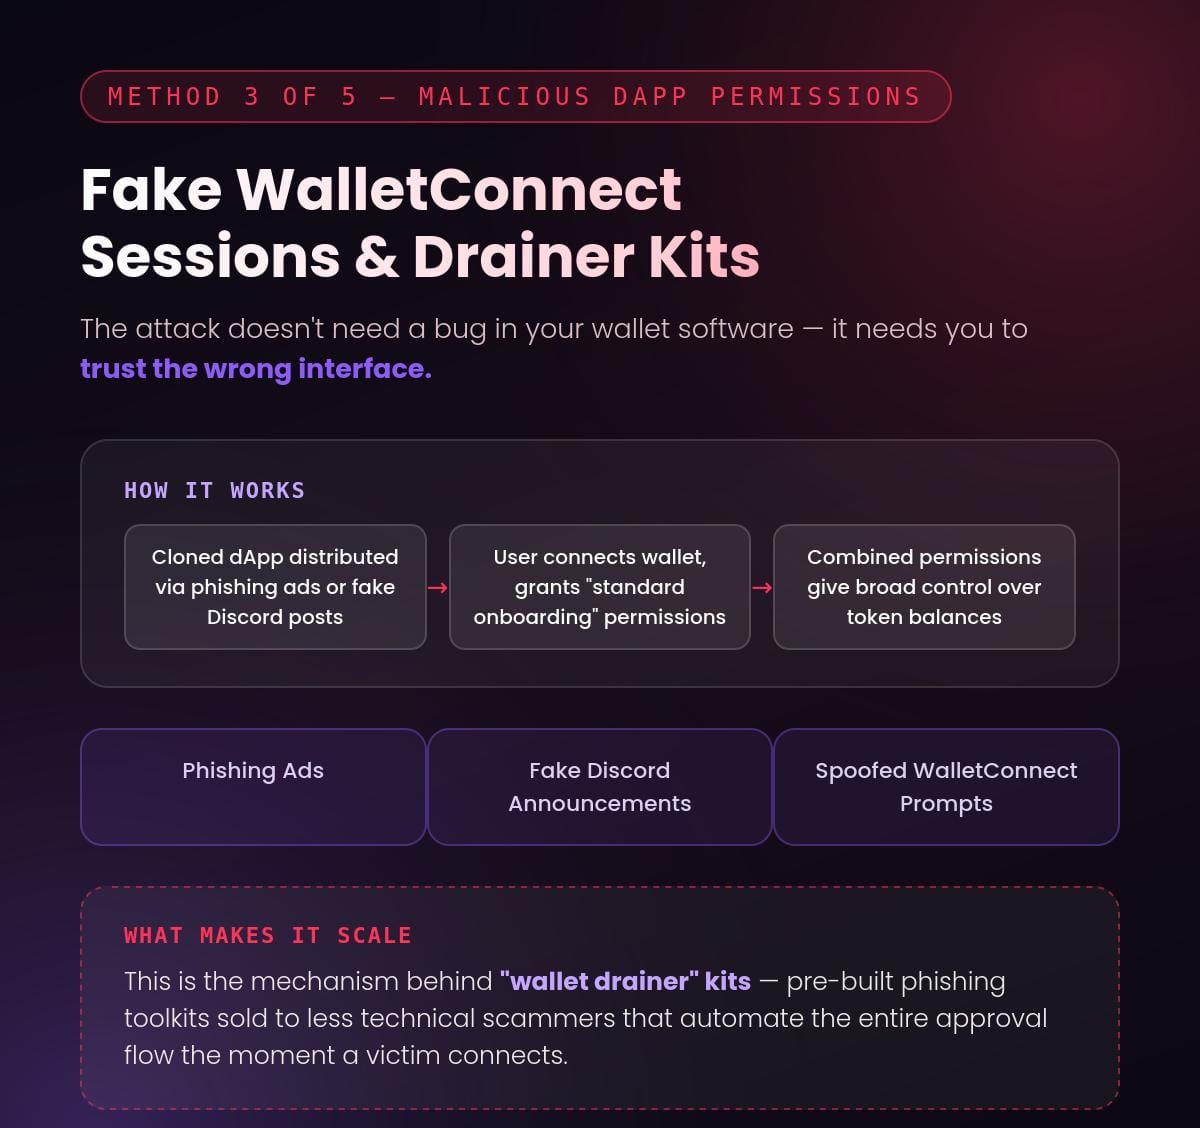
This is the underlying mechanism behind what the industry now calls “wallet drainer” kits, pre-built phishing toolkits sold to less technical scammers that automate the entire malicious approval flow the moment a victim connects. What makes this method genuinely difficult to defend against is that it doesn’t rely on any bug in MetaMask, Trust Wallet, or any other wallet software. It relies entirely on the interface convincing you that a scam site is the real thing, and every permission you grant afterward is, technically, something you authorized.
4. Address Poisoning: The Scam That Doesn’t Even Touch Your Wallet’s Permissions
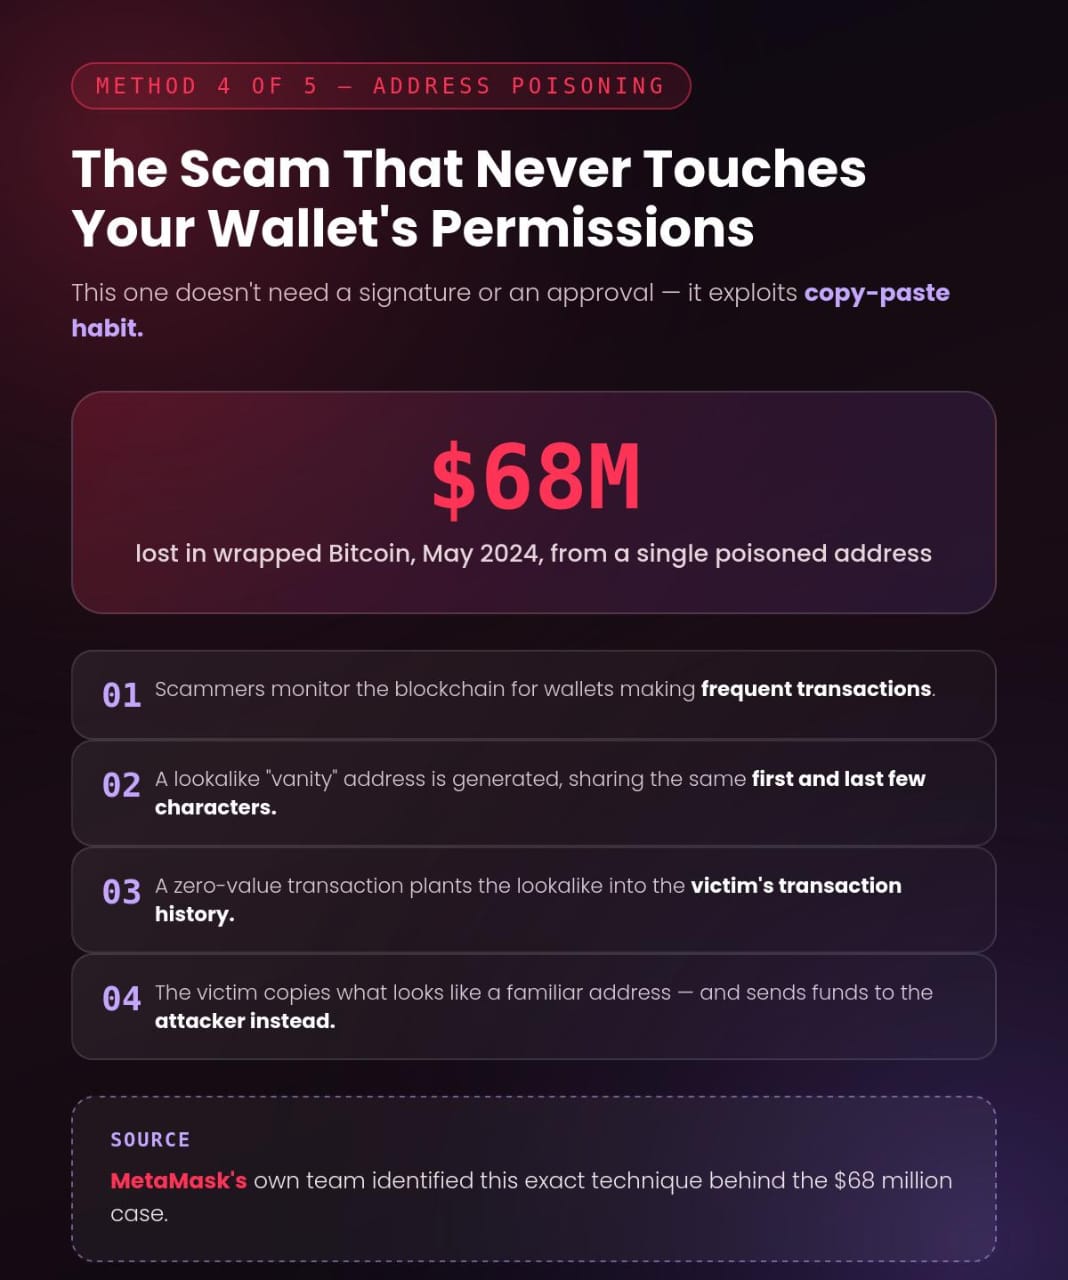
Not every method on this list requires you to sign or approve anything at all. Address poisoning works differently, and in some ways more insidiously, by exploiting simple human habit rather than any wallet mechanism. According to MetaMask’s guide on address poisoning scams, scammers monitor the blockchain for wallets making frequent transactions, then generate a lookalike “vanity” address that shares the same first and last few characters as an address the victim has genuinely interacted with before.
The attacker sends a zero-value or negligible-value transaction from that lookalike address to the victim’s wallet, which quietly plants it into the victim’s transaction history. The next time the victim goes to send funds and copies what looks like a familiar, previously used address, they may actually be copying the attacker’s poisoned lookalike instead. MetaMask’s own team has pointed to this exact technique as the mechanism behind a case in May 2024 where a single victim lost an estimated $68 million in wrapped Bitcoin after copying a poisoned address straight from their own transaction history.
5. Fake Airdrop Claims And Permit-Based Drainer Signatures
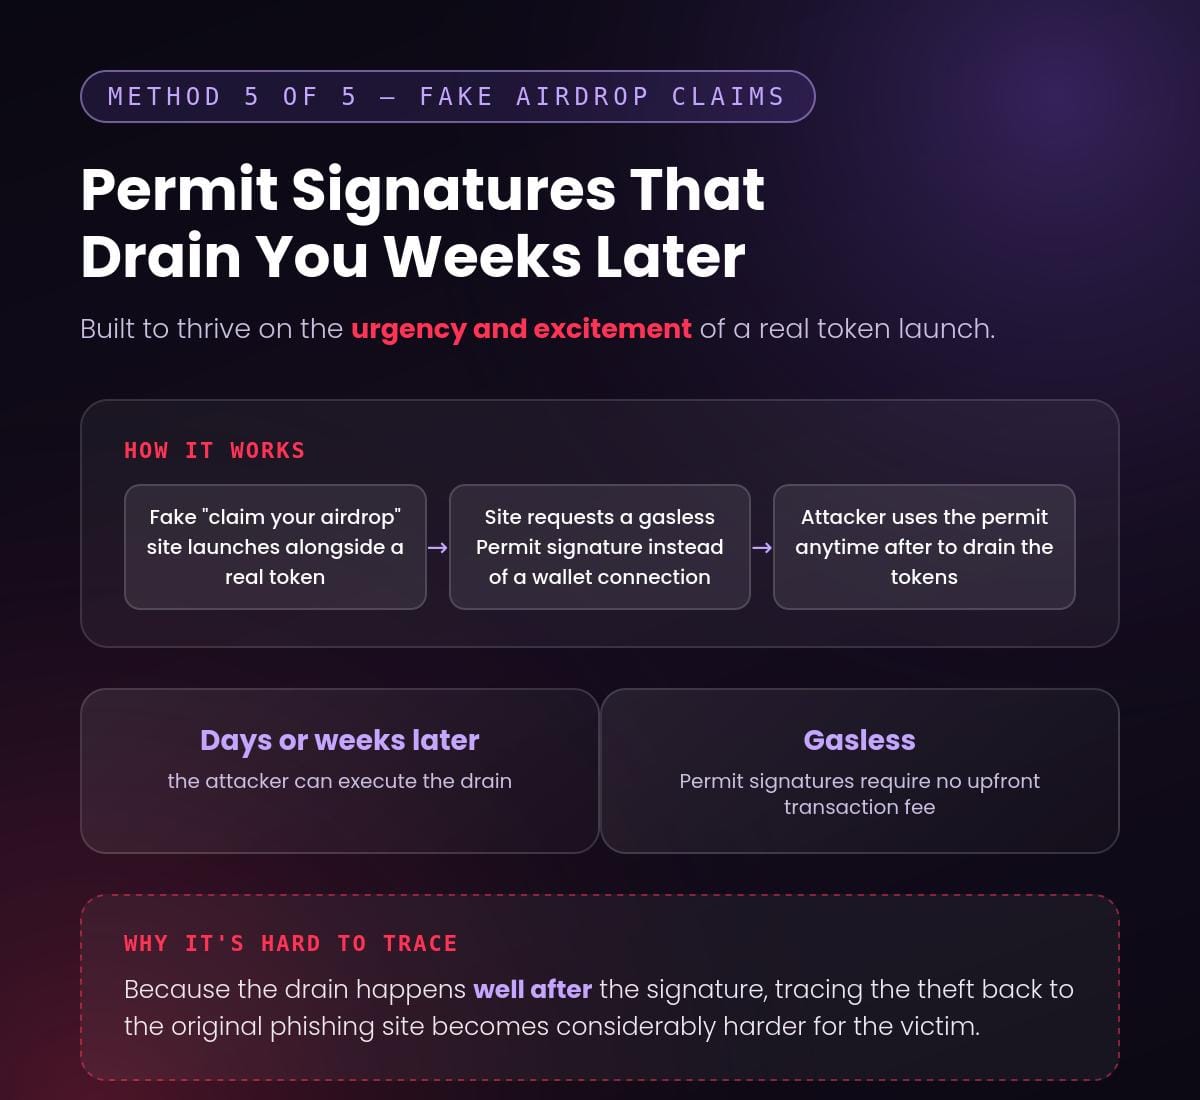
The fifth method has exploded alongside the rise of token airdrops, and it combines elements of the previous four into something particularly effective. Scammers build fake “claim your airdrop” websites, often promoted through spoofed official-looking social media accounts, timed to coincide with genuine token launches users are already anticipating. Instead of a simple wallet connection, these sites request a Permit signature, a gasless, off-chain authorization standard originally designed to make legitimate DeFi transactions more convenient.
Once signed, that permit can be used by the attacker at any point afterward to move the specified tokens out of the victim’s wallet, sometimes days or weeks later, which makes tracing the theft back to the original phishing site considerably harder for the victim. It’s a method that thrives specifically on urgency and excitement, exactly the emotional state a real airdrop announcement tends to put people in, which is precisely why scammers time these fake sites to launch right alongside genuine ones.
Lastly, reading back through all five of these, what strikes me most is that not one of them required stealing a password, cracking encryption, or getting anywhere near a seed phrase. Every single one worked because a wallet asked a question, and the victim answered it without fully understanding what they were agreeing to. If there’s one habit worth building from all of this, it’s treating every approval, signature, and connection request with the same suspicion you’d apply to someone asking for your seed phrase directly, because functionally, for the attacker, it can amount to the exact same outcome. Periodically reviewing and revoking old approvals through Etherscan’s Token Approval Checker or reading up on safety practices via MetaMask’s safety documentation costs a few minutes. Recovering funds after any of these five methods succeed usually costs everything.
Disclosure: This is not trading or investment advice. Always do your research before buying any cryptocurrency or investing in any services.
Follow us on Twitter @themerklehash to stay updated with the latest Crypto, NFT, AI, Cybersecurity, and Metaverse news!